Integration via Wiegand
The Wiegand feature enables the Akuvox device to act as a controller or a card reader.
Set it up on the web Device > Wiegand > Wiegand interface.
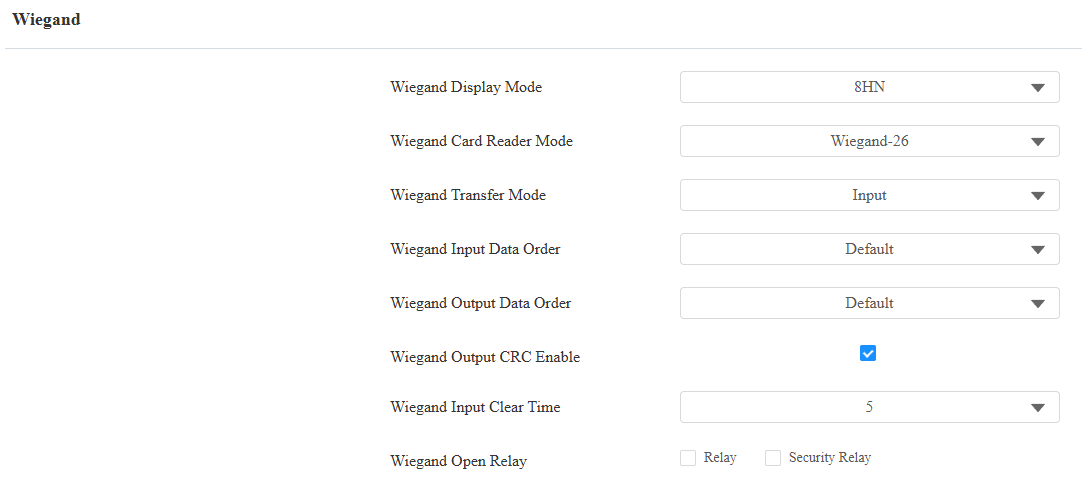
Wiegand Display Mode: Select the Wiegand card code format from the provided options: 8HN, 8H10D, 6H3D5D, 6H8D, 8HN, 8HR, RAW, and 8HR10D.
Wiegand Card Reader Mode: The transmission format should be identical between the door phone and the third-party device.
Wiegand Transfer Mode:
Input: The device serves as a relay controller.
Output: The device serves as a sender and can directly output the data, such as a card code.
Convert To Card No. Output: The device serves as a sender and cannot directly output the data, such as face data.
Wiegand Input Data Order: Set the Wiegand input data sequence between Default and Compatible. If you select Compatible, then the input card number will be reversed.
Wiegand Output Data Order: Determine the sequence of the card data after the Wiegand conversion.
For example, if the card data is 0x11 0x22 0x33 0x44 0x55, it will be 0x33 0x44 0x55 after the Wiegand conversion(e.g., Wiegand 26). If Reversed is selected, the card data is 0x55 0x44 0x33.
Wiegand Output CRC Enable: It is enabled by default for Wiegand data inspection. Disabling it may lead to integration failure with third-party devices.
Wiegand Input Clear Time: When the interval of entering passwords exceeds the time. All entered passwords will be cleared.
RF Card Verification: Available when Output or Convert to Card No. Output is selected. When enabled, the device will verify whether the card code is assigned to a user. If it is not, a prompt "Opening Door Failed" will pop up on the door phone screen. When disabled, the door phone will not perform local verification.
PIN/QR Code Verification: Available when Output is selected as Wiegand Transfer Mode. When enabled, the device will verify whether the credential is assigned to a user. If it is not, a prompt "Opening Door Failed" will pop up on the door phone screen. When disabled, the door phone will not perform local verification.
Convert To Wiegand Output: Available when Output is selected as Wiegand Transfer Mode. This option determines the output PIN format.
Disabled: Turn off the feature.
8 bits per digit: When users press "1" on the keypad, the binary data will be transmitted in 8 bits, "11100001".
4 bits per digit: When users press "1" on the keypad, the binary data will be transmitted in 4 bits, "0001".
All at once: After users enter the whole PIN code, the data will be transmitted according to the Wiegand card reader mode. For example, “123456” will be converted to “01e240” in Wiegand 26.
Note
Click here to view more information on Wiegand settings including:
Akuvox devices work as Wiegand input/output;
Wiegand Card Reader Connection.
Integration via HTTP API
HTTP API is designed to achieve a network-based integration between the third-party device and the Akuvox device.
Set it up on the web Setting > HTTP API interface.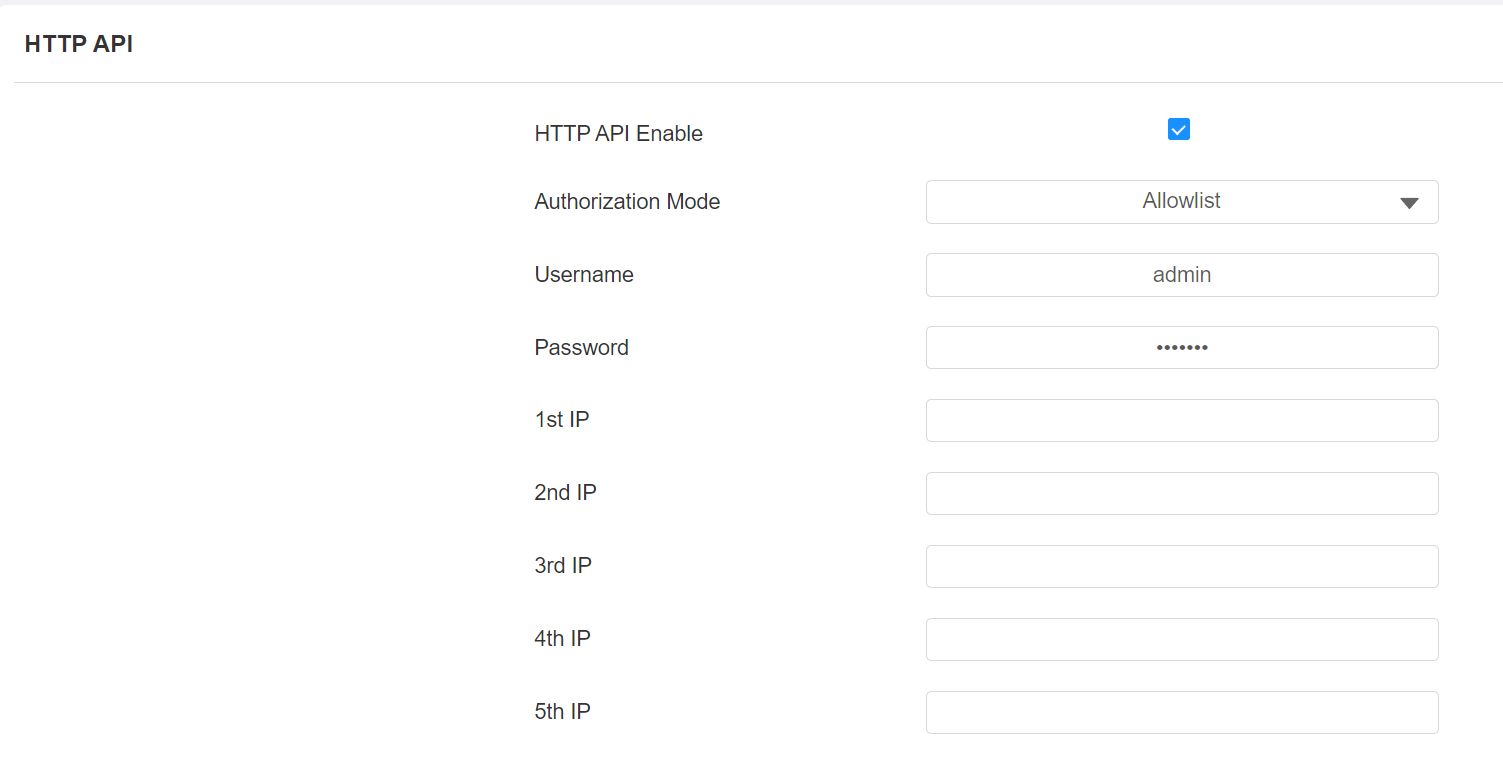
Enabled: Enable or disable the HTTP API function for third-party integration. If the function is disabled, any request to initiate the integration will be denied and return HTTP 403 forbidden status.
Authorization Mode: It is Digest by default. You are required to fill in the username and password for the authentication. In the Authorization field of the HTTP request header, use the Base64 encoding method to encode the username and password.
User Name: Enter the user name for authentication. The default is admin.
Password: Enter the password for authentication. The default is admin.
1st IP-5th IP: Enter the IP address of the third-party devices when the Allowlist authorization is selected for the integration.
Please refer to the following description for the authentication mode:
Authorization Mode | Description |
|---|---|
None | No authentication is required. This mode is intended for testing only and is not recommended in production environments. |
Allowlist | Authenticates requests based on the source IP address. Add the IP address of the third-party device to the allowlist before sending requests. Recommended for trusted LAN environments. |
Basic | Authenticates requests using a username and password. The credentials must be Base64-encoded and included in the Authorization header. |
Digest | Authenticates requests using HTTP Digest authentication. Only the MD5 algorithm is supported. |
Token | Reserved for Akuvox internal development and testing. |
Integration with Third-party Access Control Server
The device can transmit access credential data to a third-party server without doing any verification. The generation and verification of the data are conducted on the third-party server.
To set it up, go to Access Control > Relay > Third Party Integration interface.
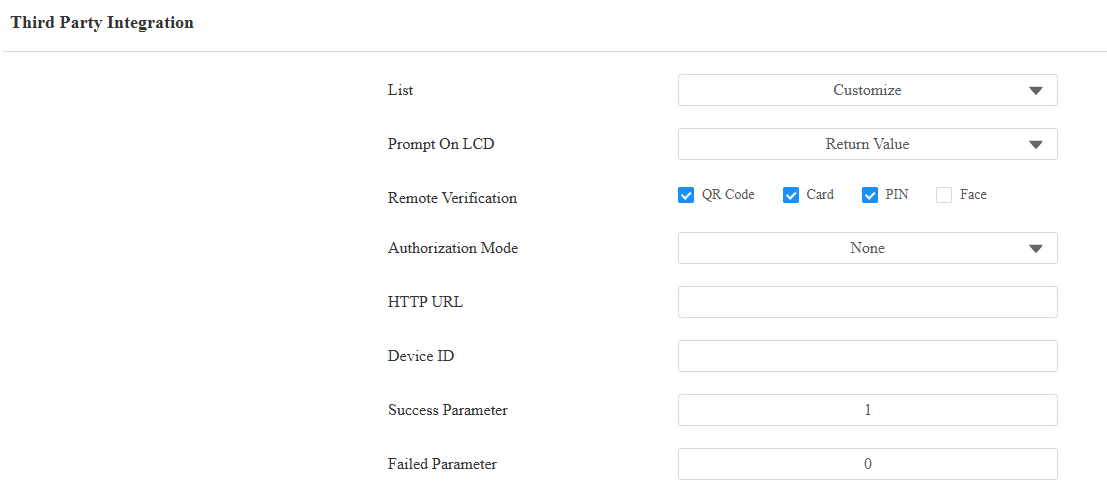
None: Disable the function.
General: Transmit the QR code-linked HTTP URL using Akuvox’s method.
HTTP URL: Enter the HTTP command format provided by the third-party service provider. After scanning the QR code, the HTTP command will carry the dynamic QR code information automatically before it is sent to the QR code server for verification. See the example: http://{Server IP}:8090/api/visitor/scan?codeKey={QRCode}&deviceId={DeviceID}.
Device ID: The device ID is provided by the third-party server. It will be added to the HTTP command automatically when using a QR code for door access.
Success Parameter: Receiving this value indicates that opening the door succeeds.
Failed Parameter: Receiving this value indicates that opening the door fails.
Customize: Transmit access credential data in a customized method. When Face is selected, the device performs local face recognition first. If no matching face is detected, authentication fails. If a match is found, the associated User ID or PIN is submitted to the third-party server for further verification.
Prompt on LCD: Select Default to adopt the Akuvox door phone’s door-opening prompt; Select Return Value to use the return value from the third-party server as the prompt.
Remote Verification: Specify which access credentials will be verified by the third-party server. In all cases, the specified credential is forwarded to the server as-is, with no local verification performed on the device.
Available options depend on the configured Authentication Mode:
Authentication Mode
Available Options
Any Method
QR Code, Card, PIN, Face
Face + PIN
QR Code, Multi-Factor
Face + RF Card
PIN + RF Card
RF Card + PIN
When a Two-Factor Authentication Mode is selected, the Remote Verification options behave as follows:
Option
Description
QR Code
The device scans the QR code and sends it directly to the third-party server.
Multi-Factor
The device first checks whether the authentication method matches the configured method.
If not matched → User is prompted to use the correct method.
If matched → The collected credentials are sent to the server for verification.
Multi-factor Authentication Request Mode: Specify how credentials collected are sent to the server under a Two-Factor Authentication Mode.
Separate Requests: The device verifies each credential separately as soon as it is provided. It does not wait for all required credentials to be entered before sending the verification request.
Single Combined Request: The device waits until all required credentials are provided, then sends them together in a single verification request.
Authorization Mode: It is used when the device sends verification requests to the server.
Basic: The request is authenticated using HTTP Basic authentication. The Username and Password are combined, encoded, and sent with each request.
Digest: The request is authenticated using HTTP Digest authentication. Instead of sending the Username and Password directly, the device sends a hash value generated from the credentials and a server-provided challenge.
HTTP URL: Enter the HTTP command format provided by the third-party service provider. After using the access credential, the HTTP command will carry the dynamic information automatically before it is sent to the server for verification. Example format:
http://{Server IP}:8090/api/visitor/scan?codeKey={QRCode}/{Card}/{UserID}/{Pin}&deviceId={DeviceID}.
If a user swipes a card, the URL will be http://192.168.35.123:8090/api/visitor/scan?codeKey={QRCode}/123456/{UserID}/{Pin}&deviceId=1.
In Two-Factor Authentication mode, the available placeholders depend on the Multi-factor Authentication Request Mode selected.
Variable
Description
{Token}
Available when Multi-factor Authentication Request Mode is set to Separate Requests. Replaced with whichever credential was collected in the current authentication step — the device sends one request per credential as it is entered.
{Card}, {Pin}, {UserID}
Available when Multi-factor Authentication Request Mode is set to Single Combined Request. {Card} is replaced with the read card number, {Pin} is replaced with the entered PIN, and {UserID} is replaced with the face-associated user ID.
{Type}
Available only under a Two-Factor Authentication Mode (both Request Modes). Indicates the two-factor authentication type:
1 = RF Card + PIN
2 = PIN + RF Card
3 = Face + RF Card
4 = Face + PIN
Device ID: The device ID is provided by the third-party server. It will be added to the HTTP command automatically.
Success Parameter: Receiving this value indicates that opening the door succeeds.
Failed Parameter: Receiving this value indicates that opening the door fails.
Note
Click here to view the detailed guide.